What Types of Hackers Could Target My Small Business?
Quick answer
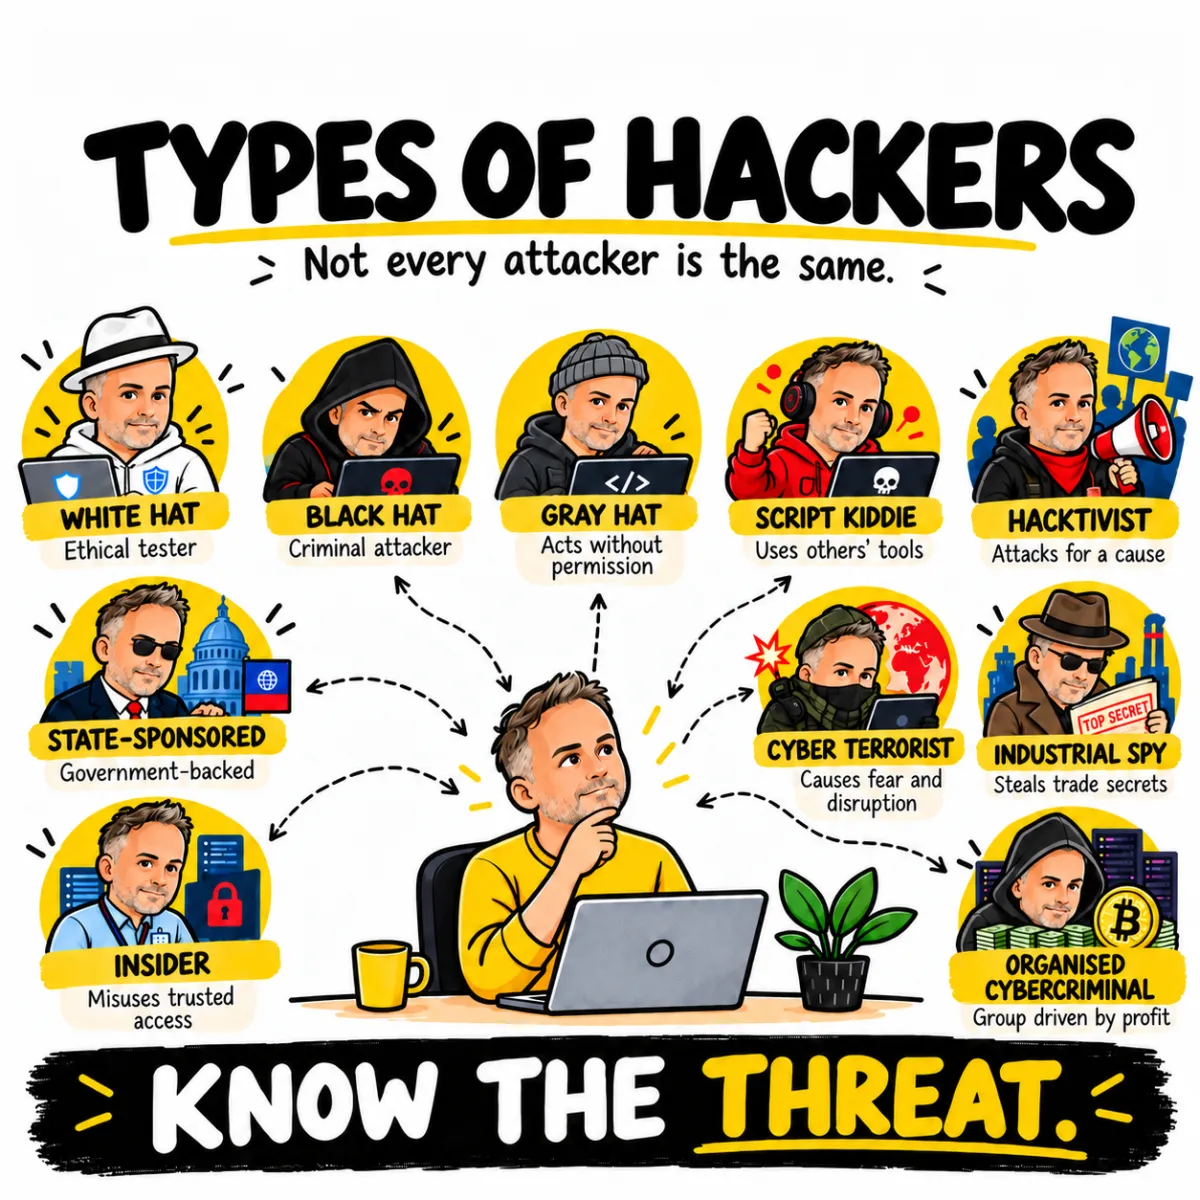
There are many different types of hackers, and they don't all have the same motivation.
Some are criminals looking for money, some are trying to steal information, some are motivated by political or social causes, and others are legitimate security professionals whose job is to find weaknesses before criminals do.
For a small business, the important thing to understand is that a hacker doesn't necessarily need to specifically target your company. Many cyber attacks are automated and simply look for weak passwords, exposed systems, vulnerable computers or poorly protected Microsoft 365 accounts.
Here are some of the main types of hackers you may hear about.
1. White Hat Hacker
What is a white hat hacker?
A white hat hacker is an ethical security professional who has permission to test systems for weaknesses.
They use many of the same techniques a criminal hacker might use, but their purpose is to help improve security rather than cause damage.
What do they do?
They might:
Test websites and networks for vulnerabilities
Check whether systems can be broken into
Perform penetration testing
Identify security weaknesses
Recommend ways of fixing them
How could they affect a small business?
Usually positively.
A small business might employ an ethical hacker or security consultant to discover weaknesses before criminals find them.
2. Black Hat Hacker
What is a black hat hacker?
A black hat hacker accesses systems without permission for malicious purposes.
Money is often the main motivation, although information theft, fraud and disruption can also be involved.
What do they do?
They may:
Steal passwords
Break into email accounts
Deploy ransomware
Steal business information
Commit financial fraud
Sell stolen information
How could they affect a small business?
A successful attack could result in stolen money, compromised Microsoft 365 accounts, lost data, ransomware or disruption to the business.
For most small businesses, this is one of the hacker types they are most likely to be concerned about.
3. Gray Hat Hacker
What is a gray hat hacker?
Gray hat hackers sit somewhere between ethical and malicious hacking.
They may discover or even access a security weakness without receiving permission first, but they aren't necessarily trying to steal information or make money from the business.
What do they do?
A gray hat hacker might discover a vulnerability on a website and then contact the company to tell them about it.
The problem is that they may have accessed something they were never authorised to access.
How could they affect a small business?
Even if their intentions aren't malicious, unauthorised testing can still cause disruption or expose sensitive information.
4. Script Kiddie
What is a script kiddie?
A script kiddie is usually someone with relatively limited technical knowledge who uses hacking tools created by other people.
They don't necessarily understand exactly how the tools work.
What do they do?
They may download tools that:
Scan the internet for vulnerable systems
Guess passwords
Attack websites
Exploit known vulnerabilities
Attempt to disrupt online services
How could they affect a small business?
This is one reason businesses can be attacked even when nobody has specifically chosen them.
Automated tools can scan thousands of systems looking for an easy way in.
If your business has an exposed system, weak password or unpatched vulnerability, it could simply appear in somebody's scan.
5. Hacktivist
What is a hacktivist?
Hacktivists use hacking to support a political, ideological or social cause.
Their motivation is normally the cause rather than financial gain.
What do they do?
They may:
Disrupt websites
Leak information
Deface websites
Carry out denial-of-service attacks
Target organisations they disagree with
How could they affect a small business?
Most small businesses are unlikely to be directly targeted by a hacktivist.
However, you could still be affected if your business works with an organisation, industry or supplier that becomes a target.
6. State-Sponsored Hacker
What is a state-sponsored hacker?
State-sponsored hackers operate on behalf of, or with the support of, a government.
They are often highly skilled and well funded.
What do they do?
Their objectives can include:
Espionage
Intelligence gathering
Stealing intellectual property
Disrupting infrastructure
Monitoring organisations or individuals
How could they affect a small business?
Most small businesses aren't the ultimate target of a nation-state attack.
But smaller organisations can sometimes become a route into a larger organisation.
For example, a criminal or state-backed attacker might compromise a smaller supplier because it has trusted access to a larger customer.
7. Insider
What is an insider threat?
An insider is somebody who already has legitimate access to the organisation.
That could be an employee, contractor, supplier or former member of staff whose access hasn't been removed.
What do they do?
An insider could:
Steal company information
Copy customer data
Leak confidential documents
Delete information
Misuse systems they are authorised to access
Not every insider incident is deliberate. Employees can also cause security incidents accidentally.
How could they affect a small business?
Small businesses often give employees relatively broad access to systems and information.
If accounts aren't properly controlled, one compromised or malicious user could potentially access a significant amount of company data.
8. Cyber Terrorist
What is a cyber terrorist?
Cyber terrorism generally refers to attacks designed to create fear, disruption or serious damage in support of an ideological or political objective.
What do they do?
Targets could include:
Government systems
Transport
Energy
Communications
Financial organisations
Critical infrastructure
How could they affect a small business?
Direct attacks against ordinary small businesses are relatively uncommon.
However, businesses can still suffer indirectly if major suppliers, communication providers or online services are disrupted.
9. Industrial Spy
What is an industrial spy?
Industrial espionage involves stealing commercially valuable information from another organisation.
The attacker may be working for a competitor, another organisation or a criminal group.
What do they do?
They may attempt to steal:
Customer lists
Pricing information
Product designs
Contracts
Business plans
Intellectual property
Tender information
How could they affect a small business?
This isn't only a big-business problem.
A small engineering company, manufacturer, technology company or professional services firm could hold commercially sensitive information that has significant value to somebody else.
10. Organised Cybercriminal
What is an organised cybercriminal?
Many serious cyber attacks are carried out by organised criminal groups rather than individuals sitting alone in a bedroom.
Modern cybercrime can operate much like a business.
Different criminals may specialise in different areas such as gaining access, stealing passwords, running ransomware or laundering stolen money.
What do they do?
They may carry out:
Ransomware attacks
Business email compromise
Invoice fraud
Password theft
Data theft
Extortion
How could they affect a small business?
This is one of the biggest threats to small businesses.
Criminal groups don't necessarily care whether your business has 10 employees or 10,000.
If they can gain access and make money from it, your business can be useful to them.
Why Would a Hacker Target a Small Business?
One of the biggest misconceptions I hear is:
"Why would anybody hack us? We're only a small business."
In reality, they may not be specifically looking for you.
Attackers can use automated systems to search the internet for businesses with:
Weak or reused passwords
Microsoft 365 accounts without suitable protection
Old or unpatched computers
Exposed remote-access systems
Poorly configured email security
Vulnerable websites
Inadequate backups
Your business doesn't have to be famous.
Sometimes an attacker simply needs to find an open door.
FOLLOW US


Systems Secure® Limited·Registered in England and Wales, company no. 07295869 6 The Meadow, Copthorne, West Sussex RH10 3RG·07702 896 910·[email protected]
How to check you’re dealing with usServing Crawley, East Grinstead, Brighton and businesses across Sussex · UK-wide remote support
COMPANY
QuantumCare
FREE TOOLS
Consulting
LEGAL
Learning Center
Copyright 2026. Systems Secure. All Rights Reserved.