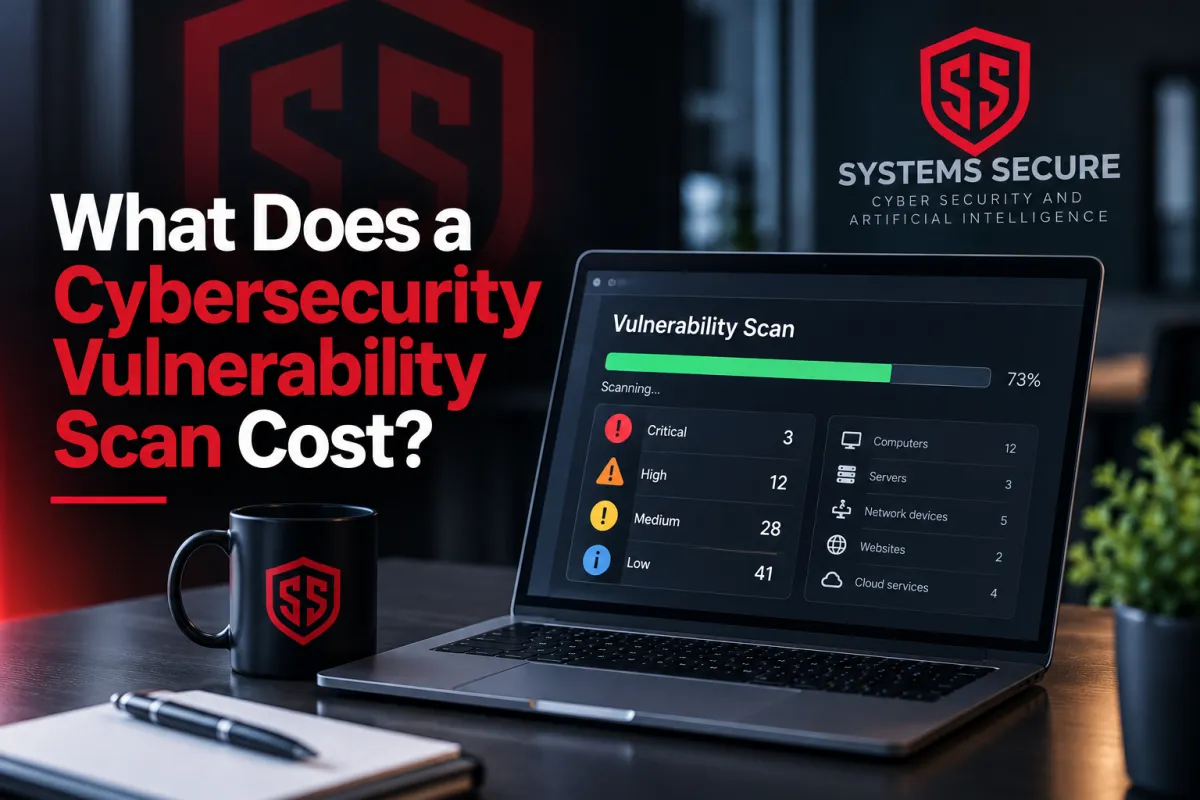
What Does a Cybersecurity Vulnerability Scan Cost?
Quick Answer
For a small UK business, the cost of a cybersecurity vulnerability scan can range from a relatively inexpensive automated scan to £1,000 or more for a properly reviewed vulnerability assessment.
The price depends mainly on:
How many computers, servers and devices need checking
Whether you need an external scan, internal scan or both
Whether cloud services are included
Whether websites or web applications need testing
Whether a cybersecurity professional reviews the results
Whether you need help fixing the problems afterwards
At Systems Secure, our cybersecurity consulting rate is £760 + VAT per day.
For a typical small-business vulnerability assessment, one to two days of work is often a sensible starting point, putting the likely cost at around:
£760 + VAT for one day
or
£1,520 + VAT for two days
The important thing is understanding what you are actually getting for that money.
A £100 automated scan and a £1,000 vulnerability assessment might both be described as a "security scan", but they are not necessarily the same service.
What is a cybersecurity vulnerability scan?
A vulnerability scan looks for known security weaknesses in your computers, servers, network equipment and other systems.
This might include things such as:
Missing security updates
Outdated software
Vulnerable services
Weak security configurations
Unnecessary services exposed to the internet
Known vulnerabilities in operating systems and applications
Network devices that should not be publicly accessible
The National Cyber Security Centre describes vulnerability scanning as an automated way of detecting security weaknesses and says it can provide a cost-effective way of finding common security problems.
https://www.ncsc.gov.uk/guidance/vulnerability-scanning-tools-and-services
The scanner compares what it finds against large databases containing known vulnerabilities.
But running the scanner is only part of the job.
Why do vulnerability scan prices vary so much?
Because the words "vulnerability scan" can describe several very different services.
At the cheapest end, somebody might simply run an automated scanner and send you the report.
At the other end, a cybersecurity consultant might:
Work out what systems you actually have
Decide what should be scanned
Carry out external and internal scans
Review the results
Remove false positives
Investigate unusual findings
Assess which vulnerabilities actually matter
Explain the risks in plain English
Prioritise what should be fixed first
Work with your IT provider to resolve them
Rescan afterwards to confirm the fixes
The computer might perform the scan.
The value comes from understanding the results.
What affects the price?
How many devices do you have?
A company with:
8 laptops
One router
Microsoft 365
No servers
is very different from a business with:
60 computers
Multiple servers
Several offices
Firewalls
Remote-access systems
Cloud servers
Public-facing applications
The larger the environment, the more there is to discover, scan and investigate.
Are you scanning externally or internally?
This is an important distinction.
External vulnerability scanning
An external scan looks at your business from the internet.
It is essentially asking:
"What can someone outside my business see and potentially attack?"
That might include:
Firewalls
VPN services
Remote-access systems
Websites
Servers
Other internet-facing services
This is useful because these are systems attackers can potentially reach without already being inside your network.
Internal vulnerability scanning
An internal scan looks at devices inside your organisation.
For example:
Computers
Servers
Printers
Network equipment
Other connected devices
This can uncover vulnerabilities that wouldn't necessarily be visible from the internet.
Both views are useful.
They answer different questions.
Why not just buy the cheapest scan?
There is nothing inherently wrong with automated vulnerability scanning.
In fact, the NCSC recommends regular vulnerability scanning as part of a vulnerability management programme. It recommends organisations carry out vulnerability assessments across their estate at least monthly.
The problem is what happens after the scanner finishes.
You could receive a report containing:
247 vulnerabilities
That sounds terrifying.
But those findings might include:
5 genuinely serious problems
20 things worth fixing
100 low-risk issues
Duplicate findings
Issues that don't apply to your environment
False positives
A business owner shouldn't be expected to work that out.
What should I get for my money?
A useful vulnerability assessment shouldn't simply give you a 150-page technical report and wish you luck.
You should be able to answer:
What did you find?
How serious is it?
What should I fix first?
How do I fix it?
What can wait?
For a small business, I would expect a good report to separate findings into something like:
Critical
Deal with these immediately.
High
Important vulnerabilities that should be addressed quickly.
Medium
Problems that should be planned for and corrected.
Low
Lower-risk improvements and housekeeping.
There should also be an explanation of why each finding matters to your particular business.
A vulnerability scanner can be wrong
This is another reason human review matters.
Automated vulnerability scanners sometimes produce false positives.
A scanner might believe a device is vulnerable when it isn't.
The opposite can also happen.
A clean vulnerability scan does not guarantee that a business is secure.
The NCSC specifically warns that automated scanners cannot detect every vulnerability and that they do not provide the same depth as appropriately skilled human testing.
That doesn't make vulnerability scanning useless.
It just means you need to understand what the tool can and cannot tell you.
Is a vulnerability scan the same as a penetration test?
No.
These are often confused.
A vulnerability scan primarily looks for known weaknesses.
A penetration test goes further.
During a penetration test, a security professional actively investigates whether weaknesses can be exploited and what an attacker might be able to achieve.
That requires considerably more manual work.
As a result, penetration testing normally costs more than vulnerability scanning.
For many small businesses, starting with a vulnerability assessment makes sense.
If something particularly important or unusual is identified, more focused testing can then be considered.
What about a £20 or £50 online vulnerability scan?
You'll find extremely cheap scanning services online.
Some are perfectly legitimate.
But understand what you're buying.
A very cheap service is likely to be highly automated.
You may receive information about your public IP address or website, but that doesn't necessarily mean your business has been assessed.
Think of it like plugging a car into a diagnostic computer.
The computer can identify problems.
But somebody still needs to understand what those results mean and decide what needs fixing.
Cybersecurity scanning is similar.
Can I run vulnerability scanning myself?
Yes.
There are both free and commercial vulnerability scanning tools available.
The NCSC provides guidance specifically designed to help organisations choose vulnerability scanning products and services.
https://www.ncsc.gov.uk/guidance/vulnerability-scanning-tools-and-services
Running the software isn't necessarily difficult.
The harder questions are:
What should I scan?
Did I scan everything?
Is the finding genuine?
How serious is it?
Could fixing it break something?
What should I fix first?
Has the problem actually been resolved?
That is where experience becomes useful.
How often should a business run vulnerability scans?
Not just once.
New vulnerabilities are discovered constantly.
Software changes.
New devices appear.
Configuration changes are made.
The NCSC recommends vulnerability assessments across an organisation's estate at least monthly, with more frequent assessments considered for particularly exposed systems.
That doesn't necessarily mean paying a consultant £760 every month.
A sensible arrangement might involve automated scanning being performed regularly, with professional review when important findings appear or as part of a scheduled cybersecurity review.
The right approach depends on the business.
Does Cyber Essentials include a vulnerability scan?
This depends on which certification you mean.
The basic Cyber Essentials certification is a verified self-assessment and does not include an additional vulnerability scan.
Cyber Essentials Plus includes technical testing, including vulnerability scanning as part of the assessment.
IASME, which operates Cyber Essentials on behalf of the NCSC, confirms this distinction in its current guidance.
https://iasme.co.uk/cyber-essentials/frequently-asked-questions/
So if somebody tells you:
"We've got Cyber Essentials, so we've already had a vulnerability scan."
that isn't necessarily correct.
Do I need a vulnerability scan if I already have an IT company?
Possibly.
Your IT company may already perform vulnerability scanning or use systems that identify vulnerabilities.
Ask them.
A useful question would be:
"Do you regularly vulnerability-scan our computers, servers and internet-facing systems, and can you show me the results?"
If they do, great.
There is no point paying someone else to unnecessarily duplicate work.
If they don't, you can have an independent cybersecurity company carry out the assessment and pass the findings to your existing IT provider.
Your IT company can then fix the problems.
You don't need to replace them.
Is a vulnerability scan worth paying for?
If you've never had one done, usually yes.
You can't fix a vulnerability you don't know exists.
One of the benefits of scanning is that it can uncover relatively ordinary problems before somebody takes advantage of them.
Things such as:
A forgotten server
An old VPN service
An unpatched computer
An exposed remote-access service
Unsupported software
A firewall service that shouldn't be public
None of these sounds particularly dramatic.
But attackers frequently exploit ordinary vulnerabilities rather than using some ingenious new hacking technique.
The NCSC describes regular scanning as an important part of understanding the risks facing an organisation.
What should I ask before paying for a vulnerability scan?
Before agreeing to anything, ask exactly what is included.
I would ask:
Are you scanning internally, externally or both?
How many devices are included?
Are servers included?
Are firewalls and network devices included?
Are cloud systems included?
Will a cybersecurity professional review the results?
Will false positives be investigated?
Will you explain what needs fixing?
Will findings be prioritised?
Is remediation included?
Will you rescan afterwards?
Will you work with my existing IT company?
Those questions make comparing quotes considerably easier.
Otherwise you could be comparing two completely different services.
How much should my small business budget?
For a straightforward small-business assessment, I would budget around one to two days of professional cybersecurity time rather than simply looking for the cheapest automated scanner.
At Systems Secure, that means approximately:
Assessment | Typical cost |
|---|---|
One day | £760 + VAT |
Two days | £1,520 + VAT |
The actual amount of work depends on what needs scanning and how complicated the environment is.
A ten-person Microsoft 365 business with laptops and one office is going to require a very different assessment from a 50-person business with multiple locations, servers and externally accessible systems.
That's why I would want to understand the environment before telling somebody exactly what they need.
What to do next
Before buying anything, start with your existing IT company.
Ask them:
"When was our last vulnerability scan, what did it cover, and can I see the results?"
You may discover that vulnerability scanning is already included in the service you're paying for.
If it isn't, or you would like an independent cybersecurity assessment, Systems Secure can review your environment and explain what we find in plain English.
We don't replace your IT company or provide general IT support.
We specialise in cybersecurity and are happy to work alongside whoever already manages your IT.
Systems Secure
In short
Vulnerability scan prices depend heavily on what is being tested
A cheap automated scan is different from a professionally reviewed assessment
External and internal scans find different types of weakness
A scanner can produce false positives, so human review matters
A vulnerability scan is not the same as a penetration test
The NCSC recommends vulnerability scanning as part of an ongoing vulnerability-management process
Basic Cyber Essentials does not include a vulnerability scan, although Cyber Essentials Plus includes technical testing
Ask your existing IT provider whether they already scan your systems
For a typical small-business professional assessment, £760–£1,520 + VAT is a sensible guide based on one to two days of Systems Secure consulting time
I particularly like this one because it can rank for the price question, while the article itself teaches the owner why a £49 scanner report and a proper vulnerability assessment shouldn't be compared purely on price.
Who checks that your security actually works?
Your IT team keeps the business running. We check it is protected — finding the risks, telling your IT team what to fix, and showing you the proof every month in plain English.
Per computer, sole trader. Excludes VAT.
- Round-the-clock monitoring of every computer
- Updates, ransomware protection, web filtering
- Training so your people spot the scams
Three packages, sized by how many people you have — £35, £204 and £710 a month. Every price is on this page.
Systems Secure Ltd is an independent cyber security company based in Copthorne, West Sussex, run by James Batt and working with businesses across the UK. Its managed service, QuantumCare, works alongside your existing IT support rather than replacing it — finding the risks, telling your IT team what to fix, and checking that important protections are still working.
This is cyber security, not IT support. Prices are published on this site, starting at £35 a month. Cyber security should give you clear answers — not long reports, confusing alerts or guesswork.
Keep your IT support. Add dedicated cyber security.
There's a reason a company's accounts are prepared by one firm and audited by another. It isn't that accountants can't be trusted — it's that nobody, however good, is well placed to check their own work.
Keeps your systems, users and everyday technology running. In-house or outsourced, they stay involved throughout — and receive clear, specific actions from us whenever their help is needed.
Finds the cyber risks, strengthens protection, and checks that important security controls are still working. You get an independent view of what's protected, what has changed, and what should happen next.
- We're not here to replace anyone or catch anyone out
- Clear responsibilities for everyone involved
- Independent checks on important protection
- Clear proof for you every month
Good IT teams tend to welcome this. An independent report is often the evidence they've been trying to get budget on for months.
Most security companies won't show you a price until you've sat through a sales call. Here's ours.
Sole Trader
One person, one computer
From £35
per computer, per month
- Round-the-clock monitoring of your computer
- Updates kept on top of automatically
- Protection against viruses and ransomware
- Dangerous websites blocked before they load
- Yearly training so you spot the scams
- Ask us a question any time
Micro Business
Priced per Microsoft 365 or Google account
From £204
per month
- Round-the-clock monitoring of every computer
- Your files backed up to the cloud
- An alert the moment a login is stolen
- Regular checks for weak spots
- Ongoing training, not just once a year
- A plain-English summary every month
Business Pro
Priced per Microsoft 365 or Google account
From £710
per month
- Everything in Micro Business
- Your network and firewall checked
- Tested from the outside, the way an attacker would
- Security policies written for you
- Cyber Essentials readiness support
- A review with James every quarter
No setup fees. No minimum contract. No penalty for changing your mind. All prices exclude VAT. Compare all packages side by side
Need security ownership at board level?
QuantumCare CISO is the mirror image of the packages above — all people, no software. A qualified security officer for a business of 10 to 250 people, from £1,200 a month. Five published prices, and no quote to ask for.
See CISO pricesNot ready for a monthly plan?
One-off work with James at a fixed price agreed before anything starts. £450 to review one system — your Microsoft 365, your firewall, your backups. £795 for the whole business. Got a question first? There's no charge for finding out whether you need us.
See consulting pricesFour steps from the price on this page to being protected
No form to fill in first, and no sales call needed to find out the number.
Pick your package
Three QuantumCare packages, sized by how many people you have, from £35 a month. Every price is published on this site.
Thirty minutes with James
A conversation, not a pitch. We confirm which package fits — and if the honest answer is that you don't need us, we'll say so.
Setup
We install it, configure it and check it is working — usually inside a week from agreement, and mostly without you noticing.
Every month after
Monitoring, updates applied in the background, and problems dealt with rather than just flagged up. Micro Business and Business Pro add a plain-English summary each month.
What you can hold us to
No lock-in
Month to month on 30 days' notice, no setup fee and no penalty for changing your mind. A 12-month option is there if you'd rather freeze your price — a choice, not a requirement.
A three-month refund
If your business is compromised while you're following the agreed security plan, you get three months' fees back. No security company can promise you'll never be attacked, and we don't.
Only 20 clients
The managed security list is capped at 20, so the person checking your security is actually paying attention — and you deal with the same person every time.
Never your competitor
We will not take on a direct competitor of an existing client, and every price on this site is the price you pay.
The proof is in the numbers, the awards and the qualifications
In IT, networks and cyber security since 1995
Systems Secure trading, full time on cyber security since 2016
Defences strengthened, risk reduced, peace of mind delivered
Trained to spot threats, stop breaches and protect businesses
The gold standard in cyber security, recognised worldwide.
Certified to run a security programme — governance, risk and reporting to a board.
Qualified to think like a hacker and find your weaknesses first.
Certified in structured cyber risk management using the NIST framework.
Globally recognised qualification in cyber security best practice.
Hi, I'm James Batt
- CISSP, C|CISO, CEH, NCSP Practitioner, Security+
- 21 years designing multi-million-dollar IT systems in oil and gas
- 16 years running Systems Secure, based in Copthorne, West Sussex
Most cyber security experts talk in acronyms. I talk like a business owner — because I am one.
I went into the oil and gas industry in 1995, doing IT, networks and security for global corporations, and led multi-million-dollar projects across America and Europe. Twenty-one years of it — and security was part of the job from the first day. I'm not an IT man who retrained into it later.
In 2010 I started Systems Secure as a sideline and ran it alongside the day job for six years. By 2016 it had outgrown the evenings and weekends, so I sat the Certified Ethical Hacker exam, left a good salary and better benefits behind, and turned the company from IT to cyber security — because security was, and still is, the weakness most smaller businesses have.
Sixteen years on, I've helped 200+ UK organisations strengthen their defences, pass compliance audits, and sleep easier knowing their data — and their reputation — are protected. You deal with me, not a rotating support desk.
Cybersecurity Essentials for Business Owners
Written for the person who owns the business, not the person who runs the servers. No acronyms, no scare stories, and nothing you need a technical background to act on.
- How attacks on businesses your size actually start — which is rarely the way people expect
- The handful of protections worth putting in place before anything else
- How to tell whether what you already have is genuinely working
We'll email you the PDF. The button opens a short form — one name, one email address.
Send me the guide In a hurry? The ten-point checklist is on the site already, with nothing to fill in.Questions you're probably asking
The main ones that come up on almost every call, answered here so you don't have to book one to find out.
How much does cyber security cost for a small business in the UK?
Systems Secure managed cyber security starts at £35 per computer per month for a sole trader, £204 per month for a business of one to nine people, and £710 per month for a business of ten or more. All prices exclude VAT and there are no setup fees.
What you pay depends on how many people you have. The Sole Trader package is priced per computer. Micro Business and Business Pro are priced per Microsoft 365 or Google account, so the cost scales with your team rather than a fixed licence block. Every price is published on the website — you don't need to sit through a sales call to find out the number.
What is QuantumCare?
QuantumCare is Systems Secure's cyber security service: three managed packages priced by how many people you have — Sole Trader from £35 a month, Micro Business from £204 and Business Pro from £710 — plus QuantumCare CISO, a separate service from £1,200 a month for businesses of 10 to 250 that need a qualified security officer rather than more software.
It is cyber security, not IT support — it works alongside whoever runs your systems rather than replacing them, finding the risks, telling your IT team what to fix, and checking that important protections are still working.
Do I have to sign a long contract?
No. Every Systems Secure package runs on a rolling monthly basis with 30 days' notice and no cancellation penalty. There is no minimum term.
A 12-month option is available if you'd rather freeze your price, which saves £2 per account per month. It's a choice, not a requirement.
Is there a setup fee?
No. There are no setup fees and nothing to pay upfront on any Systems Secure package. You pay monthly, starting from the month the service begins.
Do your prices include VAT?
No. All Systems Secure prices are quoted excluding VAT. VAT is added to your invoice at the prevailing UK rate.
Can I get a one-off piece of work instead of a monthly plan?
Yes. Fixed-price consulting is available with no ongoing commitment: £150 for a single question answered in writing within two working days, £250 for a second opinion, £450 for a review of one system, and £795 for a full review of your business. All prices exclude VAT.
These prices are built for businesses of up to 25 staff. Above that, the price rises with headcount.
Working with your IT team
Do I have to get rid of my existing IT provider?
No. Systems Secure is designed to work alongside your existing IT support, not replace it. Whether your IT is outsourced or in-house, they carry on running your systems, users and everyday technology, and receive clear, specific actions from us whenever their help is needed.
The two roles are different jobs. Your IT team keeps the business running; Systems Secure checks that it's actually protected. You get an independent view of what's protected, what has changed and what should happen next — without disrupting a relationship that's already working.
We have our own IT manager. Do we still need an outside security firm?
Usually yes — and it tends to help them rather than undermine them. An in-house IT manager is responsible for keeping everything running, which means security competes with a hundred other urgent things every week. It also means they would be reporting on the quality of their own work, which isn't a fair position to put anyone in.
Systems Secure gives your IT manager a specialist to escalate to and a second pair of eyes on the things that matter, and gives you a view that doesn't depend on one person's workload or judgement.
What is the difference between IT support and cyber security?
IT support keeps your technology working: fixing problems, setting up new starters, keeping systems online. Cyber security is a separate job — finding weaknesses before an attacker does, strengthening protection, and checking that important controls are still working months after they were switched on.
Good IT teams, in-house or outsourced, do handle parts of security — including updates, backups and access control. What they rarely provide is independent oversight: someone whose only job is to look for the gaps, and who has no reason to report that everything is fine.
My IT company says they already handle security. Do I need you as well?
Possibly not — and Systems Secure will tell you honestly if that's the case. But two things are worth knowing: nobody is well placed to audit their own work, and IT providers are themselves a target for attackers looking for a route into their customers' networks.
In a joint advisory, the UK's National Cyber Security Centre — alongside CISA, the NSA, the FBI and their Australian, Canadian and New Zealand counterparts — warned that managed service providers are granted privileged access to a customer's network, which can create opportunities for attackers.
That isn't hypothetical. In July 2021 attackers exploited a flaw in Kaseya VSA, remote management software used by IT providers, and reached an estimated 800 to 1,500 businesses through around 60 providers. None of those businesses did anything wrong. They were reached through a supplier they trusted.
So the question worth asking isn't "do you handle security?" It's "when did you last check that it's working, and can I see the evidence?"
Risk and threats
Is my business too small to be a cyber target?
No. In the last 12 months, 46% of UK small businesses and 42% of micro businesses identified a cyber security breach or attack, according to the Government's Cyber Security Breaches Survey 2025/26.
Most attacks aren't personally chosen — they're automated. Software scans the internet looking for weaknesses and takes whatever it finds. A business with three staff and a website nobody visits still gets probed daily. Phishing remains by far the most common method, experienced by 38% of businesses.
Isn't antivirus enough?
No. Antivirus catches known threats, but most modern attacks don't rely on a recognisable file. Phishing, stolen passwords and misconfigured settings all bypass antivirus entirely.
Proper protection needs several layers: monitoring that spots unusual behaviour, multi-factor authentication, patching, backups you've actually tested, and staff who can recognise a convincing fake email.
Isn't cyber insurance enough on its own?
No. Most cyber insurance policies require you to prove you took reasonable precautions — multi-factor authentication, staff training, patch management. If you can't demonstrate those, a claim can be reduced or refused entirely.
Insurers increasingly expect standards such as Cyber Essentials before they'll offer cover or renew it. Insurance is worth having, but it pays out after the damage. It doesn't prevent it.
What happens if we get attacked anyway?
No security company can promise you'll never be attacked, and Systems Secure doesn't make that promise. What it does offer is a three-month refund guarantee: if your business is compromised while you're following the agreed security plan, you get three months' fees back.
The realistic goal is fewer incidents, caught earlier and contained faster.
The service
What do I actually get each month?
Every package includes round-the-clock monitoring, automatic updates, protection against viruses and ransomware, blocking of dangerous websites, and staff training. Larger packages add cloud backup, alerts when a login is stolen, regular checks for weak spots, firewall and network reviews, written security policies and a quarterly review.
Micro Business and Business Pro also include a short monthly summary showing what's protected, what changed and what needs attention — written in plain English rather than as a long technical report.
What size businesses do you work with?
From sole traders up to businesses of around 250 staff. There are three packages: Sole Trader for one person, Micro Business for one to nine people, and Business Pro for ten to 250. Business Pro has a minimum of ten accounts.
Do you only work with businesses in West Sussex?
No. Systems Secure is based in Copthorne, West Sussex, and works with businesses across the UK. Almost all of the work is done remotely, so your location doesn't affect the service or the price.
On-site visits are available and charged separately: £240 for a visit of up to two hours, £400 for a half day and £760 for a full day.
Can you help us get Cyber Essentials?
Yes. Cyber Essentials readiness support is included in the Business Pro package. That means reviewing your current setup against the requirements, telling you what needs to change, and getting you to the point where you can pass.
Worth knowing: Cyber Essentials reflects the day of assessment, not a permanent state. Ongoing patching, access reviews and vulnerability checks are what keep the certificate meaningful between renewals.
Who you're dealing with
Who will I actually be dealing with?
James Batt. Systems Secure deliberately caps its managed security client list at 20, so you deal with the same person every time rather than a rotating support desk.
Systems Secure will also never take on a direct competitor of an existing client.
What qualifications does James Batt hold?
James Batt holds CISSP, C|CISO (Certified Chief Information Security Officer), CEH (Certified Ethical Hacker), NCSP Practitioner and CompTIA Security+.
Behind those: 21 years designing multi-million-dollar IT systems for the oil and gas industry, and 16 years running Systems Secure. The company was named Cybersecurity Company of the Year at the West Sussex Business Awards 2025, and Security Solution Specialists of the Year at the E2 Media Awards 2025.
Why do you only take on 20 clients?
Because security oversight is only worth paying for if someone is genuinely paying attention. Capping the list at 20 clients means each one gets real scrutiny rather than an automated dashboard nobody reads.
It also means Systems Secure can be honest about capacity rather than selling a service it can't properly deliver.
Thirty minutes, free, and nothing to decide on the call
A conversation, not a pitch. We'll confirm which package fits — and if the honest answer is that you don't need us, we'll say so.
FOLLOW US


Systems Secure® Limited·Registered in England and Wales, company no. 07295869 6 The Meadow, Copthorne, West Sussex RH10 3RG·07702 896 910·[email protected]
How to check you’re dealing with usServing Crawley, East Grinstead, Brighton and businesses across Sussex · UK-wide remote support
COMPANY
QuantumCare
FREE TOOLS
Consulting
LEGAL
Learning Center
Copyright 2026. Systems Secure. All Rights Reserved.